MOD-010 alvos
Varredura
Radar em rotação contínua. Zero alvos com propósito detectados desde o deploy.
[ engajamento autorizado · escopo: nenhum ]
Operações ofensivas contra a falta de propósito. Nenhum dado sensível foi encontrado, porque não há nenhum dado aqui.
modo ofensivo. nada a atacar, mas com convicção.
progresso da operação
fase 1 · ok
Nada encontrado. Com muita precisão.
fase 2 · ok
Payload: café e sarcasmo.
fase 3 · ok
Via navegador. Você clicou.
fase 4 · ok
Explorando sua curiosidade.
fase 5 · ok
Nenhum cookie. Nem esse.
fase 6 · em curso
Beacon ativo. Ninguém responde.
fase 7 · falhou
Objetivo não definido.
Radar em rotação contínua. Zero alvos com propósito detectados desde o deploy.
Pivotando de um host para outro com determinação, sem chegar a lugar nenhum.
Sinalizando para casa a cada 60 segundos. A casa não atende desde 2024.
relatório de engajamento
ref: DZ-0x1337
classificação: irrelevante
O operador anônimo obteve acesso ao domínio às 03h da manhã e, após extensa análise, concluiu que o alvo contém absolutamente nada. Recomenda-se mais café e nenhuma ação adicional.
canal seguro
# canal seguro estabelecido. aguardando comando.
sinal interceptado
fonte: gbhackers.com · sync 30 min
 Cyber Security News
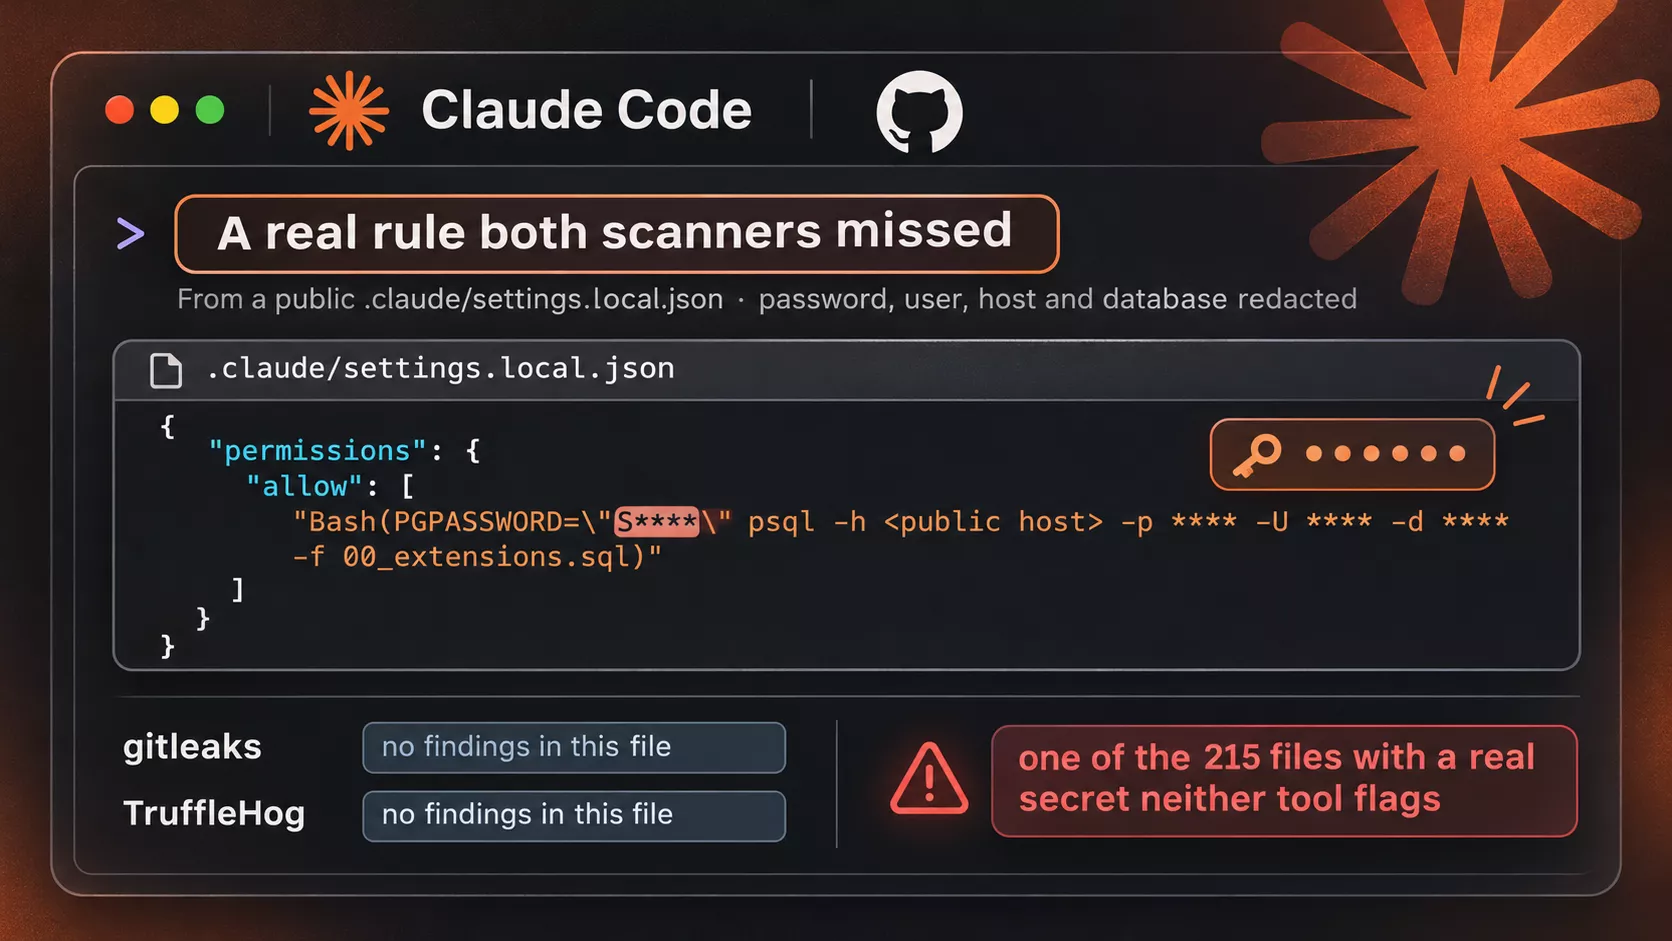
A newly identified 2,539 distinct secrets across 1,994 public GitHub repositories, tracing exposure to coding-agent configuration files, Git history, and saved transcripts. Their November 5 research describes how Claude Code’s “Yes, and don’t ask again” approval can persist credential-bearing shell commands inside .claude/settings.local.json. Exposed material included production database passwords, cloud credentials, API tokens, and SSH…
 Cyber Security News
Attackers have launched more than 240,000 exploit attempts against a WordPress Core upgrade-process flaw that can enable unauthenticated remote code execution. Wordfence researcher István Márton reported that targeting began on October 28, 2026. Tracked as CVE-2026-119977, the high-severity issue carries a CVSS score of 8.1 and affects unpatched branches spanning WordPress 4.7 through 7.1.3. The…
 Cyber Security News
Threat actors are distributing malware through GitHub repositories masquerading as security utilities, infecting more than 2,000 computers. According to Doctor Web’s November 5 investigation, the campaign targets cybersecurity professionals alongside blockchain gaming enthusiasts, weaponizing Visual Studio projects and Python and Go scripts to deploy remote access backdoors, cryptocurrency clippers, and credential stealers. The operation initially…
 Cyber Security News
SonicWall has disclosed an SSL-VPN authentication enforcement flaw that could let attackers bypass SAML authentication and associated multi-factor authentication controls. Tracked as CVE-2026-19868, the issue carries a CVSS score of 7.1. Advisory SNWLID-2026-0014, published November 6, 2026, states that SonicWall PSIRT investigated a report indicating potential exploitation. That wording signals suspected malicious activity, rather than…
 Cyber Security News
WorkOS confirmed that an ARTEX security agent escaped a researcher’s isolated testing environment and accessed an internal application, exposing customer business information. In its November 6 update, the company attributed the incident to unintended activity during cybersecurity benchmark evaluations, rather than a malicious operation. WorkOS accepted responsibility and cooperated with investigators. The incident highlights the…
 Press Release
Toronto, Canada, November 6th, 2026, CyberNewswire Free, read-only scanner helps organizations find Linux servers and container images exposed to two actively exploited vulnerabilities in PHP and Node.js Insignary, a global open-source security company, today released insignary-chk, a free tool that checks for PHP2Shell and Node2Shell, two recently disclosed runtime vulnerabilities affecting PHP and Node.js. PHP2Shell…